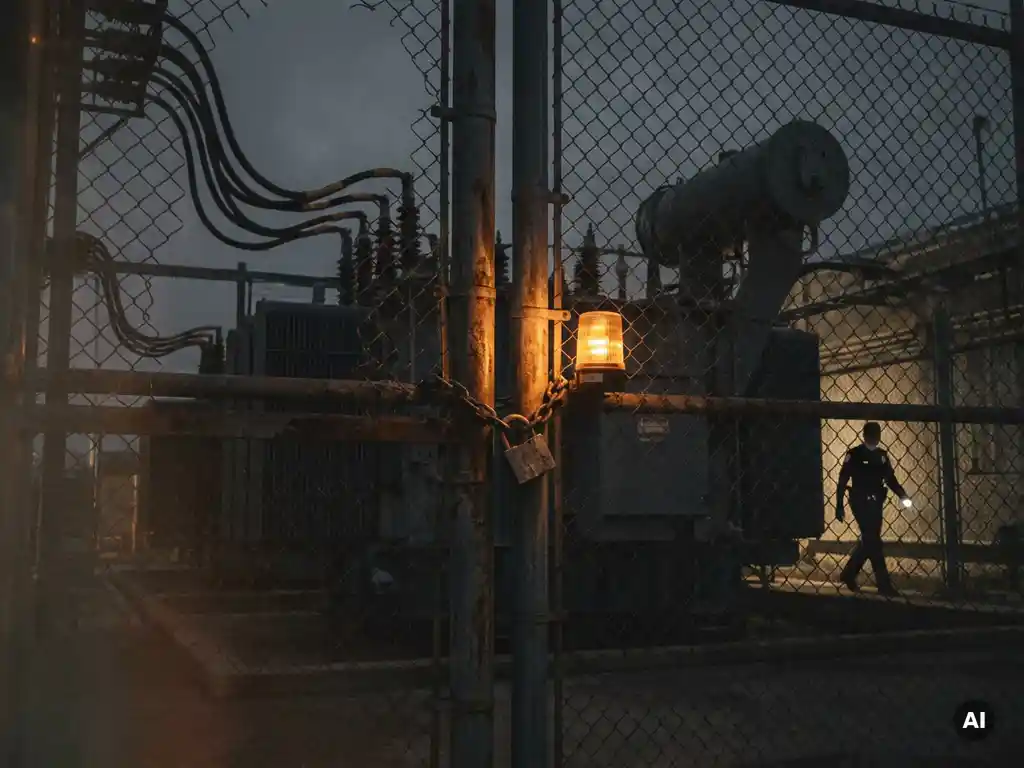
How do you prevent sabotage of vital infrastructure?
Sabotage of vital infrastructure is prevented by a combination of physical security, strict access control, early detection and clear response procedures. No single measure is sufficient on its own: effective protection requires a layered approach where technology, people, and processes work together. Would you like to know how your organization can put this into concrete practice? Feel free to contact us with Sellox. In this article, we answer the most frequently asked questions about securing critical infrastructure.
What is meant by vital infrastructure?
Vital infrastructure encompasses all systems, networks, and facilities whose failure or disruption would have serious societal consequences. Examples include energy supply, drinking water, transport, telecommunications, financial systems, and healthcare. When one of these sectors fails, citizens, businesses, and government agencies are directly affected in their functioning.
The Dutch government maintains an official list of vital sectors that is periodically reviewed. In addition to traditional physical infrastructure, digital infrastructure is increasingly falling under this definition. Data centers, industrial control systems, and critical software platforms are thus becoming just as relevant as a power plant or a water management facility. In practice, the distinction between physical and digital vital infrastructure is blurring rapidly, as most physical systems are now digitally controlled.
What forms of sabotage threaten vital infrastructure?
Critical infrastructure is threatened by both physical and digital sabotage. Physical sabotage includes the deliberate damage to installations, the manipulation of equipment, or the disruption of logistics chains. Digital sabotage focuses on infiltrating networks, disabling industrial systems, or spreading malware in critical control software.
In addition to external threats, internal sabotage poses an underestimated risk. Employees or contractors with access to sensitive systems can cause damage, whether intentionally or unintentionally. Other forms of sabotage include:
- Physical attacks on transformer stations, pumps, or communication towers
- Cyberattacks via phishing, ransomware, or attacks on industrial control systems
- Supply chain sabotage in which components or software are manipulated before delivery
- Insider threats by employees with malicious intent or under external pressure
- Hybrid attacks that combine physical and digital methods
The threat from state actors and organized criminals is increasing. In 2026, security experts foresee a clear increase in targeted, long-term attacks in which saboteurs first scout undetected before striking.
Who is responsible for the protection of critical infrastructure?
Responsibility for the protection of critical infrastructure is shared between the government and private parties. The central government establishes the legal framework and the national threat analysis, while owners and operators of vital facilities are themselves responsible for the operational security of their installations.
In the Netherlands, the National Coordinator for Counterterrorism and Security (NCTV) coordinates the approach at the national level. Sectoral supervisory bodies, such as the Netherlands Authority for Nuclear Safety and Radiation Protection or the Human Environment and Transport Inspectorate, oversee compliance within specific domains.
For organizations in the private sector, this means that they cannot rely on government security alone. They are legally and morally obligated to take adequate security measures themselves, conduct risk analyses, and cooperate with relevant government agencies in the event of incidents. Collaboration between public and private parties, also known as public-private partnerships, is indispensable in this regard.
How do you detect sabotage of vital infrastructure early?
Early detection of sabotage begins with the continuous monitoring of both physical locations and digital systems. Anomalous behavior, unusual access attempts, unexplained malfunctions, or suspicious presence around an object are signals that must be recognized and acted upon immediately.
Physical detection methods
Camera systems with image analysis, motion sensors, fence detection, and regular physical inspections form the basis of early physical detection. Security personnel trained to recognize suspicious behavior add a human layer that technology cannot fully replace. Furthermore, access movement logs provide insight into who was at a location and when.
Digital detection methods
On the digital side, Security Information and Event Management (SIEM) systems, network intrusion detection, and anomaly detection are essential. These systems continuously analyze traffic patterns and trigger an alarm in the event of deviations. Industrial networks require specific solutions in this regard, as standard IT security tools are not always compatible with operational technology (OT).
Which security measures best protect critical infrastructure?
The most effective security of critical infrastructure combines physical access security, digital protection, and organizational measures in a layered system. No single measure is foolproof; the strength lies in the combination and coordination of the layers.
Essential measures include:
- Access control: Strictly regulating who has access to which zones, systems, and information is one of the most fundamental security measures. Well-configured access control prevents unauthorized persons from gaining access to critical components.
- Perimeter and site security: Fencing, barriers, lighting systems, and security restrict physical access to sensitive locations.
- Network segmentation: By strictly separating operational networks from office networks, you limit the damage that a digital attack can cause.
- Multi-factor authentication: Multi-factor authentication is a basic requirement for access to critical systems.
- Consciousness training: Employees who recognize threats and know how to act form an active line of defense.
- Regular risk analyses and penetration tests: By proactively detecting vulnerabilities, organizations can close security gaps before an attacker finds them.
What should you do if sabotage is suspected or discovered?
If sabotage is suspected or discovered, you must act immediately according to a pre-established incident response plan. This means: documenting the incident, alerting the appropriate internal and external parties, limiting the damage, and securing evidence for further investigation.
Specifically, you go through the following steps:
- Alert immediately: Inform the person responsible for security and, depending on the severity, also the police, the National Cyber Security Centre (NCSC), or other relevant authorities.
- Limit the damage: Isolate affected systems or zones to prevent further spread or damage, but act only within the limits of the incident response plan.
- Document everything: Record what was observed, when, and by whom. This is crucial for forensic investigation and for improving security afterwards.
- Securing evidence: Do not change the situation until authorized investigators are on site, unless immediate safety risks require it.
- Evaluate and improve: Following the handling of the incident, a thorough analysis will follow regarding how the sabotage was possible and which adjustments will strengthen security.
A good incident response plan is not something you draw up the moment something goes wrong. Regular exercises and scenario analyses ensure that everyone knows their role when it really matters.
Do you want to have the security of your critical infrastructure professionally assessed or strengthened? Contact us contact Sellox for a no-obligation consultation.
Do you want to know what this looks like in your sector? Read how Sellox sets up access for data centers and critical IT, for government and public space and for defense and high-assurance environments. Or present your situation directly to us via the contact form.
Frequently Asked Questions
How often should an organization review its security plan for critical infrastructure?
A security plan for critical infrastructure must be reviewed at least annually, but also after every significant incident, a major organizational change, or a change in the threat landscape. Threats evolve rapidly, meaning a static plan can become outdated within just a few months. Combine the annual review with regular penetration tests and exercises to continuously assess the effectiveness of the plan.
What are the most common mistakes when securing critical infrastructure?
One of the most common mistakes is treating physical and digital security as two separate domains, whereas they are inextricably linked. Other common errors include underestimating insider threats, lacking a tested incident response plan, and neglecting supply chain security. Organizations often focus on technical measures but forget that untrained personnel remain one of the greatest vulnerabilities.
Which laws and regulations apply to organizations that manage vital infrastructure?
In the Netherlands, organizations managing critical infrastructure are bound by, among other things, the Network and Information Systems Security Act (Wbni), which implements the European NIS2 Directive. Depending on the sector, additional sector-specific regulations and oversight by authorities such as the ANVS or the ILT may apply. It is strongly recommended to seek legal and security advice to ensure full compliance, as non-compliance can lead to fines and increased liability.
How do you address the security of older, outdated systems (legacy systems) within critical infrastructure?
Legacy systems pose a particular challenge because they often cannot be patched or easily replaced, yet they perform critical functions. An effective approach combines network segmentation to isolate these systems, additional monitoring to quickly detect anomalies, and compensating measures such as strict physical access control. In the longer term, a phased migration plan to more modern, more secure systems is inevitable.
How do you effectively involve employees in the security of critical infrastructure?
Effective employee engagement begins with targeted awareness training that goes beyond annual e-learning: think of realistic exercises, phishing simulations, and practical scenarios that align with their daily work. Additionally, ensure a safe reporting culture where employees can report suspicious situations without hesitation. Employees who understand why security is important and what their personal role is in it form an active and valuable line of defense.
What is the difference between a Business Continuity Plan (BCP) and an incident response plan, and do you need both?
An incident response plan focuses on the immediate response during and immediately following a security incident: detection, containment, communication, and evidence safeguarding. A Business Continuity Plan (BCP) focuses on ensuring business continuity in the longer term, so that critical processes can continue as much as possible even during a severe disruption. For organizations managing vital infrastructure, both are indispensable and must be aligned to ensure a seamless transition from crisis response to recovery and continuity.
When does it make sense to engage an external security partner for the protection of critical infrastructure?
An external security partner is valuable when internal knowledge or capacity is lacking, when an objective assessment of current security is needed, or when specialized expertise is required for specific threats such as OT security or advanced cyberattacks. External partners can also assist with conducting risk analyses, penetration tests, and developing or testing incident response plans. Always choose a partner with demonstrable experience in the relevant sector and familiarity with applicable laws and regulations.